Router>en Router#conf t Enter configuration commands, one per line. End with CNTL/Z. Router(config)#int f0/0 Router(config-if)#ip add 192.168.1.254 255.255.255.0 Router(config-if)#no sh
Router(config-if)# %LINK-5-CHANGED: Interface FastEthernet0/0, changed state to up
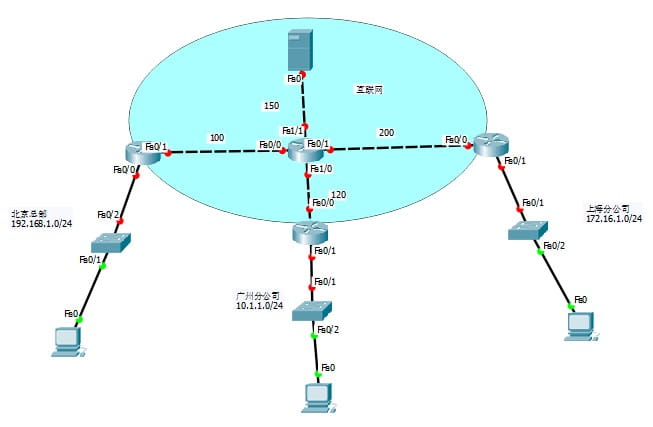
%LINEPROTO-5-UPDOWN: Line protocol on Interface FastEthernet0/0, changed state to up exit Router(config)#int f0/1 Router(config-if)#ip add 100.1.1.1 255.255.255.0 Router(config-if)#no sh Router(config-if)# %LINK-5-CHANGED: Interface FastEthernet0/1, changed state to up exit Router(config)# %LINEPROTO-5-UPDOWN: Line protocol on Interface FastEthernet0/1, changed state to up Router(config)#int f0/1 Router(config-if)#ip route 0.0.0.00.0.0.0100.1.1.2 /*创建传输集*/ Router(config)#crypto isakmp policy 1 /*对称加密算法*/ Router(config-isakmp)#encryption aes /*DH算法的长度*/ Router(config-isakmp)#group 2 /*使用预共享秘钥进行加密和身份验证*/ Router(config-isakmp)#authentication pre-share /*验证数据完整性*/ Router(config-isakmp)#hash sha /*生存时间*/ Router(config-isakmp)#lifetime 86400 Router(config-isakmp)#exit /*隧道标识,用于区分隧道*/ Router(config)#crypto isakmp key password address 200.1.1.2 /*使用ACL对VPN流量进行过滤*/ Router(config)#access-list 100 permit ip 192.168.1.00.0.0.255172.16.1.00.0.0.255 /*定义数据连接的算法和传输名*/ Router(config)#crypto ipsec transform-set kctran esp-aes esp-sha-hmac /*创建MAP映射表kcmap*/ Router(config)#crypto map kcmap 1 ipsec-isakmp % NOTE: This new crypto map will remain disabled until a peer and a valid access list have been configured. Router(config-crypto-map)#match address 100 Router(config-crypto-map)#set transform-set kctran Router(config-crypto-map)#set peer 200.1.1.2 Router(config-crypto-map)#exit Router(config)#int f0/1 Router(config-if)#crypto map kcmap *Jan 307:16:26.785: %CRYPTO-6-ISAKMP_ON_OFF: ISAKMP is ON Router(config-if)#exit Router(config)#
配置NAT(PAT)
北京总部
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
Router>en
Router#conf t
Enter configuration commands, one per line.  End with CNTL/Z.

/*对两个内网IP流量做NAT豁免*/
Router(config)#acc 101 deny ip 192.168.1.0 0.0.0.255 172.16.1.0 0.0.0.255
Router(config)#acc 101 permit ip any any
Router(config)#int f0/0
Router(config-if)#ip nat inside
Router(config-if)#exit
Router(config)#int f0/1
Router(config-if)#ip nat outside
Router(config-if)#exit
Router(config)#ip nat inside source list 101 int f0/1 overload
Router(config)#
上海分公司
1
2
3
4
5
6
7
8
9
10
11
/*对两个内网IP流量做NAT豁免*/ Router(config)#acc 101 deny ip 172.16.1.0 0.0.0.255 192.168.1.0 0.0.0.255 Router(config)#acc 101 permit ip any any
Router>en Router#conf t Enter configuration commands, one per line. End with CNTL/Z. Router(config)#crypto isakmp policy 1 Router(config-isakmp)#encryption aes Router(config-isakmp)#group 2 Router(config-isakmp)#authentication pre-share Router(config-isakmp)#lifetime 86400 Router(config-isakmp)#hash sha Router(config-isakmp)#exit Router(config)#crypto isakmp key password address 100.1.1.1 Router(config)#acc 100 permit ip 10.1.1.0 0.0.0.255 192.168.1.0 0.0.0.255 Router(config)#crypto ipsec transform-set kctran esp-aes esp-sha-hmac Router(config)#crypto map kcmap 1 ipsec-isakmp % NOTE: This new crypto map will remain disabled until a peer and a valid access list have been configured. Router(config-crypto-map)#set transform-set kctran Router(config-crypto-map)#set peer 100.1.1.1 Router(config-crypto-map)#match address 100 Router(config-crypto-map)#exit Router(config)#int f0/0 Router(config-if)#crypto map kcmap *Jan 307:16:26.785: %CRYPTO-6-ISAKMP_ON_OFF: ISAKMP is ON Router(config-if)#exit
Router>en Router#conf t Enter configuration commands, one per line. End with CNTL/Z. Router(config)#do sh acc Extended IP access list 100 10 permit ip 192.168.1.00.0.0.255172.16.1.00.0.0.255 (2match(es)) Extended IP access list 101 10 deny ip 192.168.1.00.0.0.255172.16.1.00.0.0.255 (12match(es)) 20permit ip any any(10 match(es)) Router(config)#ip access-list extended 101 Router(config-ext-nacl)#15 deny ip 192.168.1.0 0.0.0.255 10.1.1.0 0.0.0.255 Router(config-ext-nacl)#exit Router(config)#acc 102 permit ip 192.168.1.0 0.0.0.255 10.1.1.0 0.0.0.255 /*第二条隧道标识和身份验证*/ Router(config)#crypto isakmp key password address 120.1.1.1 Router(config)#crypto map kcmap 2 ipsec-isakmp % NOTE: This new crypto map will remain disabled until a peer and a valid access list have been configured. Router(config-crypto-map)#set transform-set kctran Router(config-crypto-map)#set peer 120.1.1.1 Router(config-crypto-map)#match add 102 Router(config-crypto-map)#exit
Router(config)#acc 100 permit ip 10.1.1.0 0.0.0.255 172.16.1.0 0.0.0.255
总部允许广州的数据包通过
1
2
3
4
5
6
7
8
9
10
11
12
13
Router#conf t Enter configuration commands, one per line. End with CNTL/Z. Router(config)#do sh acc Extended IP access list 100 10 permit ip 192.168.1.00.0.0.255172.16.1.00.0.0.255 Extended IP access list 101 10 deny ip 192.168.1.00.0.0.255172.16.1.00.0.0.255 20 deny ip 192.168.1.00.0.0.25510.1.1.00.0.0.255 (20match(es)) 30permit ip any any(2 match(es)) Extended IP access list 102 10 permit ip 192.168.1.0 0.0.0.255 10.1.1.0 0.0.0.255 (9 match(es)) Router(config)#acc 100 permit ip 10.1.1.0 0.0.0.255 172.16.1.0 0.0.0.255 Router(config)#
上海配置ACL,用于回包
1
2
3
4
5
6
7
Router(config)#acc 100 permit ip 172.16.1.0 0.0.0.255
/*由于部署了NAT,还需要做NAT豁免,否则数据包一到公网就被干掉*/
Router(config)#ip acc extended 101 Router(config-ext-nacl)#11 deny ip 172.16.1.00.0.0.25510.1.1.00.0.0.255 Router(config-ext-nacl)#exit
最后总部做一条ACL,允许上海向广州回包
1
Router(config)#acc 102 permit ip 172.16.1.0 0.0.0.255 10.1.1.0 0.0.0.255

 微信